


Why a large hospital chose Redblock to reduce identity exposure and bring disconnected applications into its IGA.


Real-time account aggregation

4-week POV

No Tickets. No CSVs.


Overview
Achieving quarterly visibility into identities, roles, and entitlements became a significant barrier to governing applications for a large US-based healthcare organization. Because a substantial portion of their application ecosystem lacked APIs, the team was forced to rely on CSV exports and manual IT support tickets to aggregate application identity data.
To reduce identity exposure across disconnected applications, the organization sought a solution capable of bridging the gap between its IGA platform and these target systems. Their existing workflow created heavy operational friction, as cumbersome data extraction, manual ETL processing, and delayed post-review access changes often took weeks to complete.
Following a competitive evaluation, the provider selected Redblock for its AI agents, which automatically retrieve identity data and execute approved remediation steps directly within target applications. Redblock successfully demonstrated automated account aggregation and real-time remediation during the evaluation.
Transitioning from quarterly governance to near-real-time enforcement
The organization’s primary objectives were risk reduction and minimizing identity exposure across applications unmonitored by their existing IGA platform. While their security strategy focused on expanding visibility and policy enforcement across all applications, the lack of native API connectivity presented a major obstacle. The end-to-end access review process depended heavily on IT tickets and manual data extractions by system administrators from app consoles—a workflow taking days or weeks per application. Crucially, the IGA platform received no automated confirmation when remediation decisions were fulfilled.
The stakes were high: each manual IT ticket and unverified CSV contributed to compliance backlogs while increasing exposure in the event of an incident.
Manual efforts fragmented identity data and expanded the attack surface. Recognizing these vulnerabilities, the security team sought a fundamental shift—moving from a reactive quarterly process to a proactive, real-time identity inventory and automated offboarding of unneeded accounts.
The team evaluated several alternatives, including custom API integration development for internal and third-party apps, as well as RPA tools. However, RPA solutions proved too generic for specialized identity management tasks, and building custom APIs for many web applications was infeasible. The organization required a drop-in solution that could seamlessly extend their existing IGA infrastructure while eliminating manual operations.
Core requirements for solution selection

Automated aggregation of identities, roles, and entitlements
A complete replacement for manual, CSV-driven identity aggregation across disconnected applications.

Real-time remediation of identity changes after access reviews
Automated propagation of access review decisions from the IGA to target applications without manual intervention.

Inline transformation of data from source before IGA
Automatic attribute completion and data transformation without requiring manual overhead prior to IGA ingestion.

No data leaves their defined network boundary
Execution of the Redblock AI infrastructure strictly within the organization's secure network boundary.
Leveraging Agentic AI for a successful proof of value
The company selected Redblock due to its unique architectural approach. Redblock’s computer-use AI agents, capable of executing complex tasks directly within application interfaces, provided the key breakthrough. Unlike legacy methods relying on manual spreadsheet manipulation, Redblock ingests live data directly from applications once authorized, immediately surfacing it for access reviews, workflows, and anomaly detection.
This shift enabled the team to transition from constantly reconciling identity discrepancies between system logs to actively removing orphan accounts.
By automating bidirectional identity synchronization, they established an instantaneous, verifiable access management flow.
To validate the architecture, the organization executed a four-week Proof of Value (POV) focused on verifying Redblock’s performance across their primary use cases and key performance indicators.
Core systems architecture for the POV
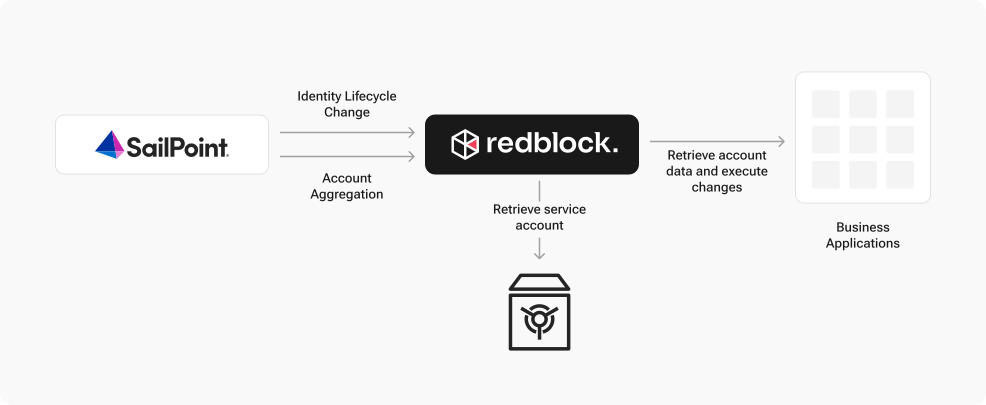
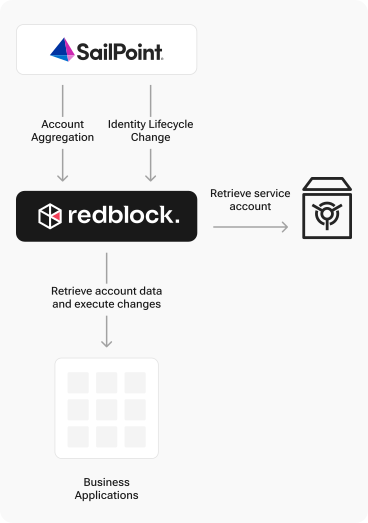
Integration architecture: Redblock integrates directly with the customer’s existing IGA platform to enable real-time aggregation and remediation across the enterprise application ecosystem.
Mitigating identity risk across every enterprise application
Following the successful POV, the organization selected Redblock to support its long-term strategy of bringing all enterprise applications and identities under centralized visibility and control. While the initial phase focused on replacing manual workflows across key applications to accelerate lifecycle operations and reduce exposure, projected operational savings from eliminating CSV processing and IT tickets strongly reinforced the business case.
For this customer, Redblock serves as more than an extension to their IGA platform—it forms the foundation of their identity exposure management architecture, ensuring every identity, role, and entitlement is visible and updated in real time according to policy.
Close Your IAM Blast Radius.
See how Redblock replaces ticket-driven identity execution with continuous lifecycle enforcement across your application estate.